Agentic capability for the SIEM you already run

AI agents work your security queue.
You approve.

Overwatch Console gives your team specialist AI agents that triage incidents, check each other's work, tune noisy rules and hunt. Every verdict shows its evidence, and nothing consequential happens until you say so.

Supports Microsoft Sentinel. Elastic and Splunk in development. 7-day demo with a fictional company; your 14-day trial starts when your Sentinel workspace connects.

Overwatch Console // Live demo

Every Verdict Shows Its Work

The queries Dax ran, what came back and why it decided.

A Second Opinion Built In

Demitry, on a different model, checks risky calls before anything is acted on.

Your Logs Stay in Your SIEM

Agents query your workspace on demand. We store their findings, not your raw logs.

Works with Microsoft Sentinel Supported Elastic Security In development Splunk In development

See Exactly What the Agents Did

Real screens from Overwatch Console, recorded with a fictional demo company.

Investigation

Watch Dax think, one query at a time.

Before every query Dax writes down why it is running it: the hypotheses in play, what a result would prove and what it would rule out. You see each step, the rows that came back and the verdict with its confidence. Expand any step for the exact query.
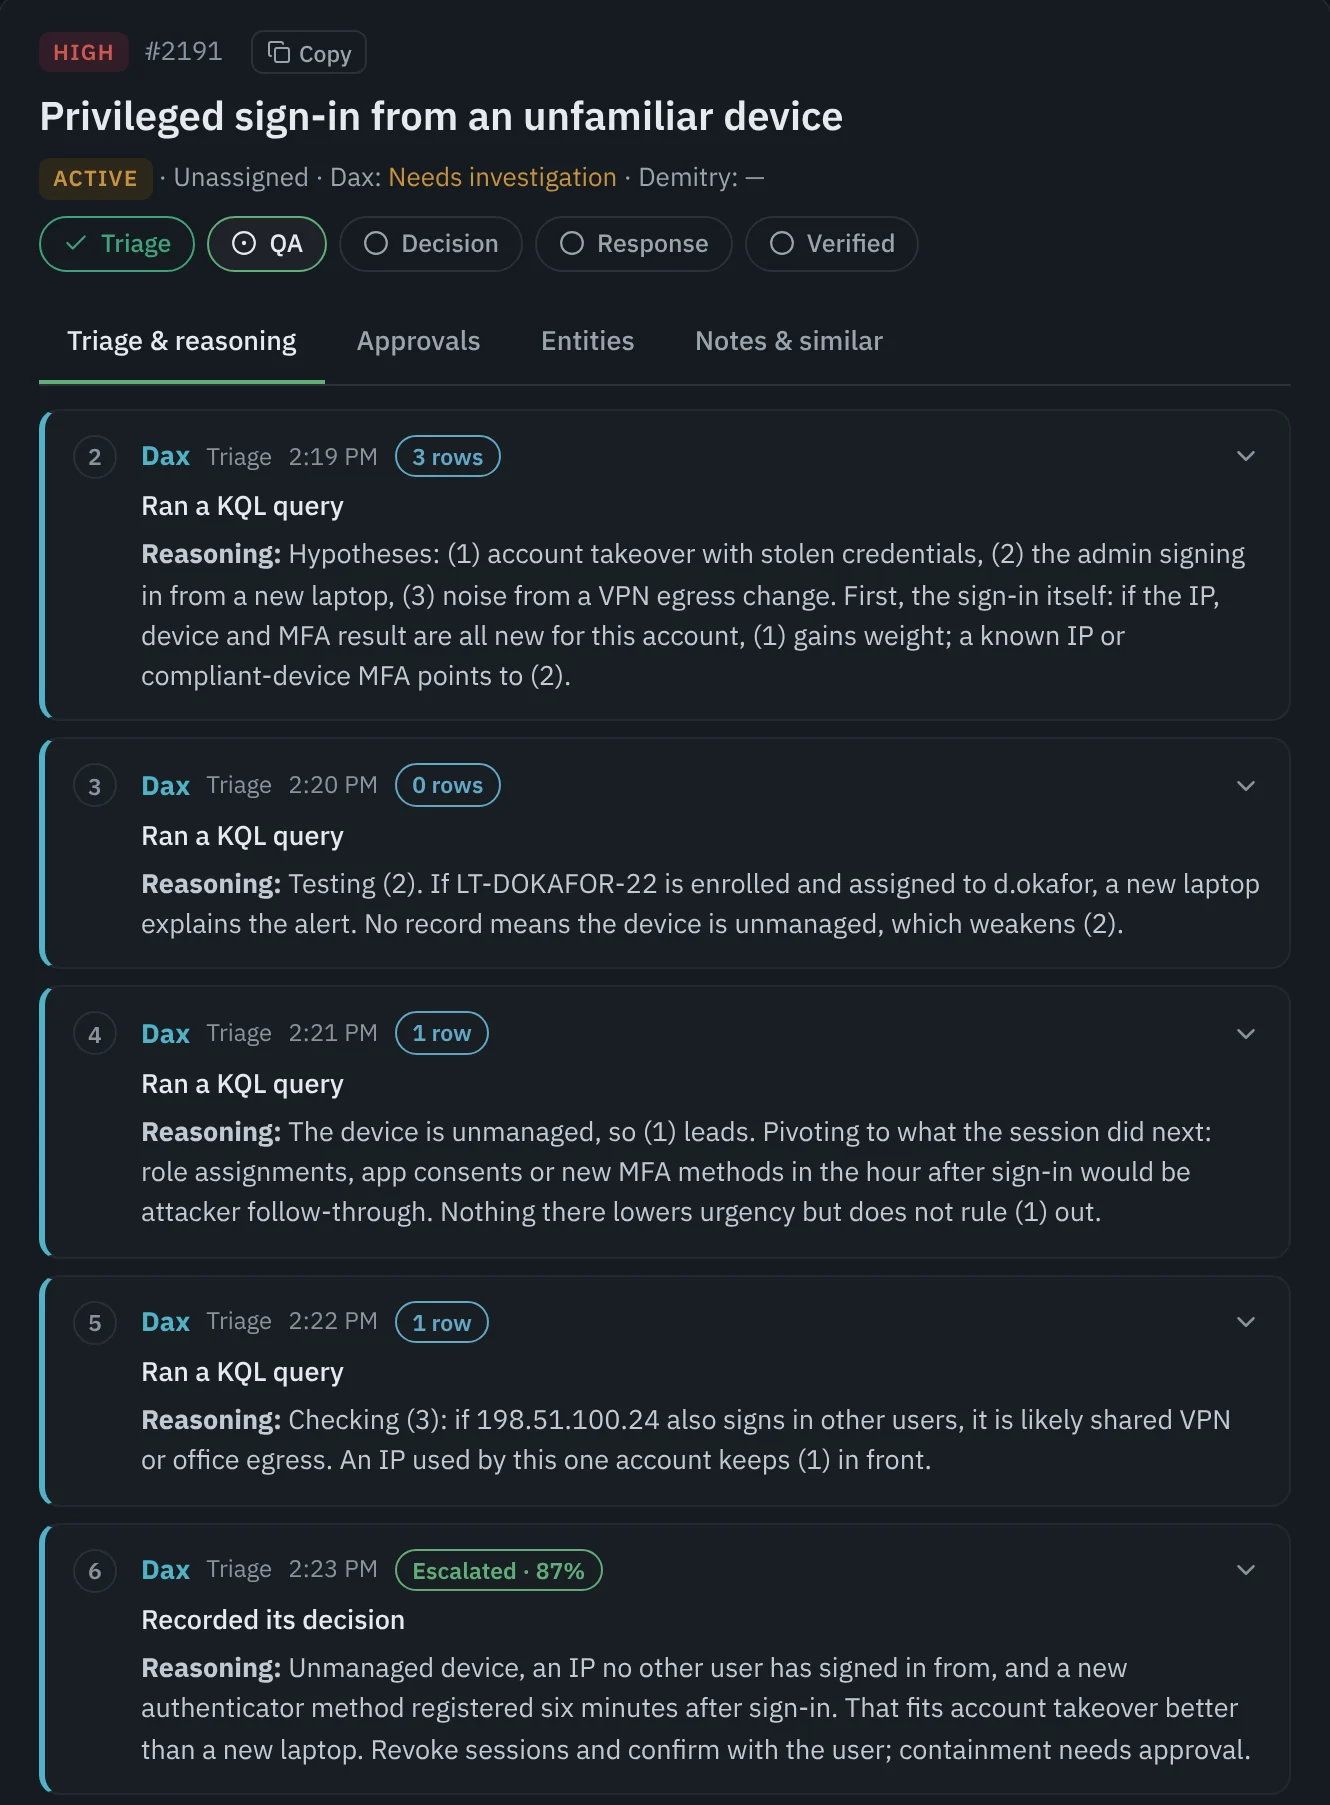
A privileged sign-in case: Dax's reasoning before each KQL query, testing account takeover, a new laptop and VPN noise in turn, ending in an escalated verdict at 87% confidence
Approvals

Nothing consequential happens until you approve.

Isolations, disabled accounts, closes, rule tunes and deploys queue here with Dax's analysis, Demitry's review and the policy that applies. Approve, deny or comment. Your decision is recorded either way.
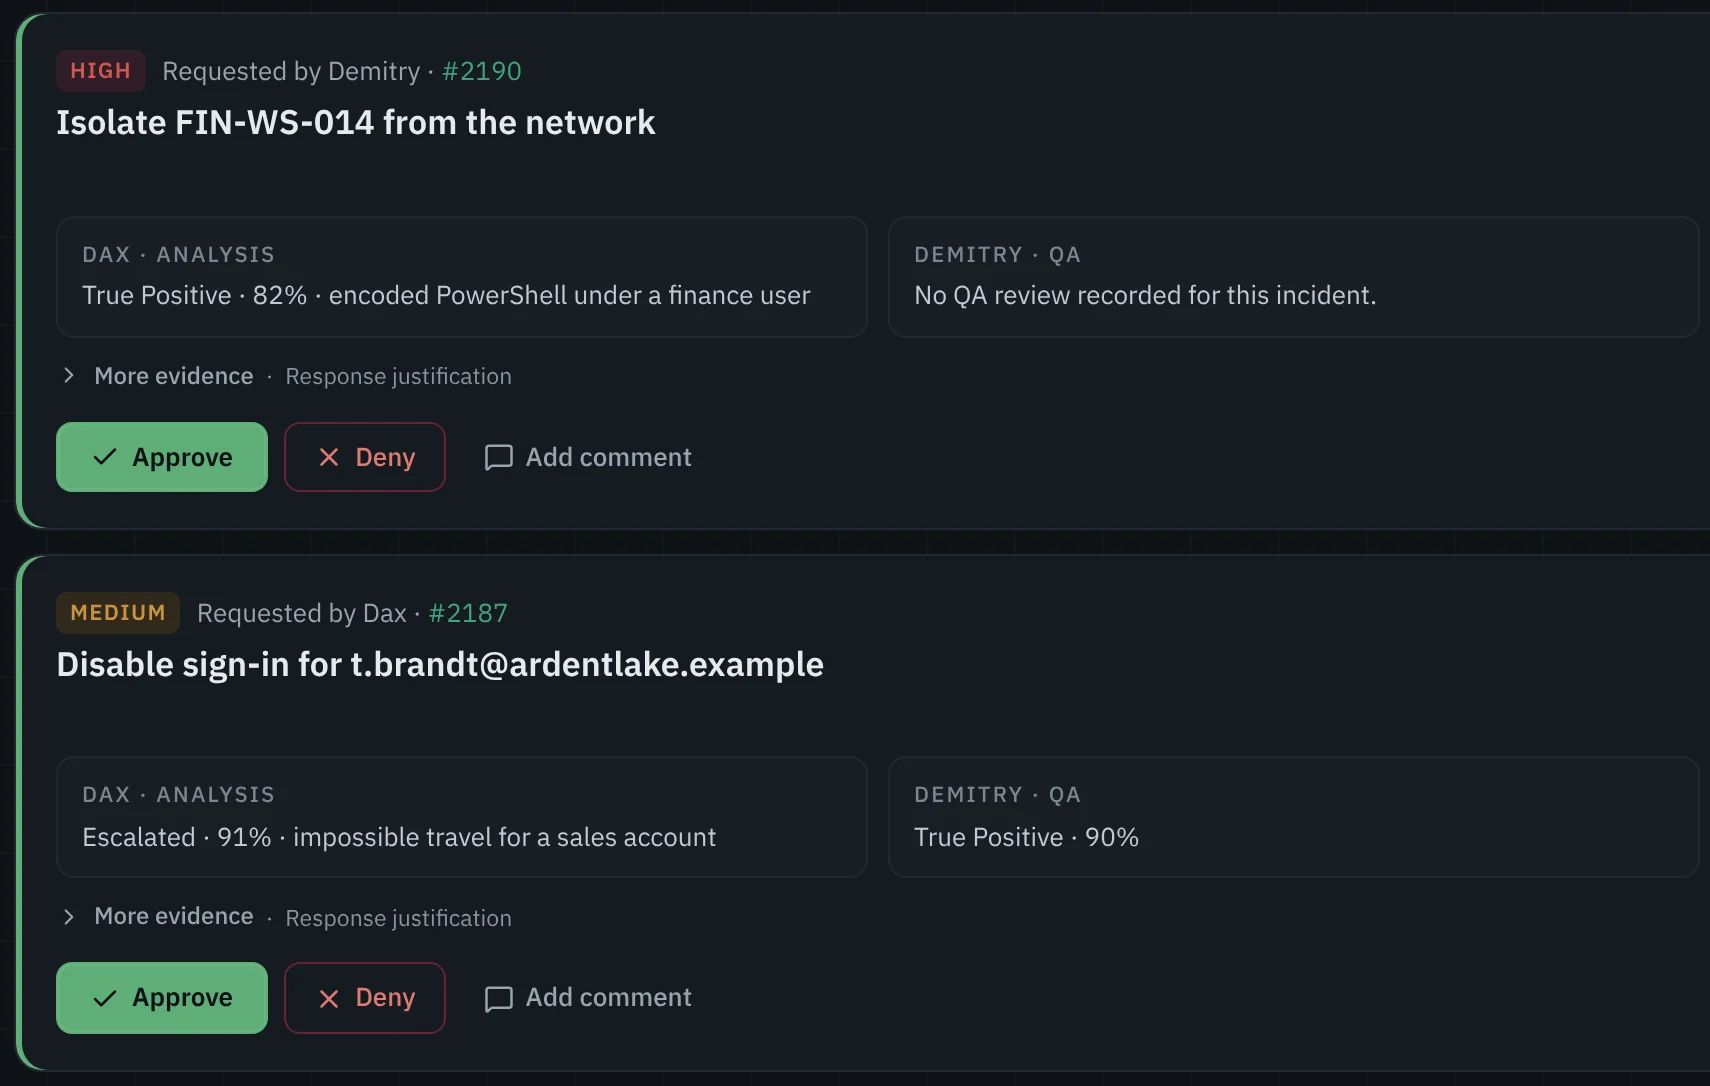
Two pending approvals, isolating a workstation and disabling a sign-in, each with Dax's analysis, Demitry's QA and Approve or Deny
Audit Trail

A record nobody can quietly edit.

Every agent step and human decision is written to an append-only, hash-chained ledger. Open any record to see what happened and why, re-verify the chain any time and export it for your auditors.
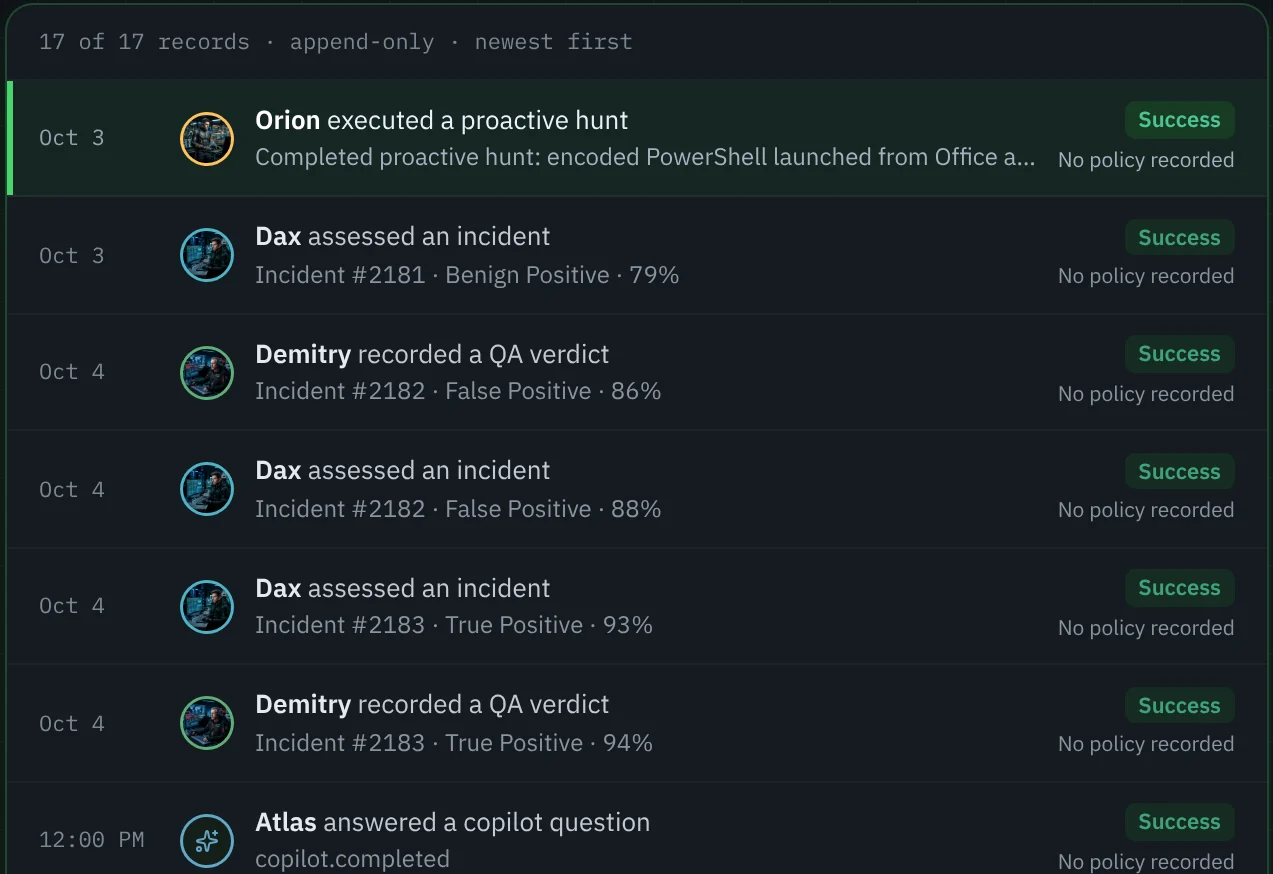
The append-only activity ledger: hunts, verdicts, QA reviews and reports from each agent, newest first

One Incident, Start to Finish

Each agent owns one job. Here is what happens when your SIEM raises an alert.

  1. 01

    Your SIEM raises an incident

    A new incident lands in your workspace.

  2. 02

    Dax investigates

    Runs the KQL it needs and records a verdict with every query, result and reason.

  3. 03

    Demitry checks

    A second agent on a different model reviews risky or low-confidence calls.

  4. 04

    You decide

    Closes, tunes and response actions wait in Approvals with the evidence attached.

  5. 05

    Done, on the record

    Closed, contained or escalated, and written to the audit trail.

The Rest of the Team

Marien Tuning

Finds noisy rules and proposes fixes, replaying each change against past incidents first.

Renzo Detections

Turns fresh threat intelligence into KQL detections mapped to MITRE ATT&CK.

Orion Hunting

Runs read-only hunts across your workspace and surfaces findings for review.

Caleb Malware

Analyzes suspicious files and writes up the verdict, what to do now and the indicators.

Maxwell Deploys

Deploys and recalls detection rules after you approve them, with version history for rollback.

Atlas Copilot

Answers questions about your incidents, detections and agent work in plain language.

Hand Over as Much as You Trust

Start with every consequential action waiting for you. Loosen it one action at a time, only when the record earns it.

Default

Approval mode

Agents investigate and propose. Every close, tune, rule deploy and response action waits for a person.

When you're ready

Per-action autonomy

An admin lets specific actions run on their own, one action type at a time. Everything else still waits.

Overnight

3am containment

Allow containment to run on its own inside the guardrails you set, then review it in the morning.

Software your team runs. You own incident response. We keep the platform up and correct and support you during business hours.
8 Specialist AI Agents
0 Raw Logs Stored by Overwatch
14 Day Trial on Your Own Sentinel

We Take Malware Apart and Publish the Detections

Research and detections from our own analysis, free to use.

Certified. Proven. Battle-Tested.

Our team holds elite-tier certifications from the industry's most respected bodies, with hands-on experience at the highest levels of national cyber defense.

OSCP OSCP Offensive Security
AZ-500 Azure Security Engineer Microsoft Certified
BTL2 Blue Team Level 1 + 2 Security Blue Team
CySA+ CySA+ CompTIA
Security+ Security+ CompTIA
PMRP Malware Research Professional TCM Security
OSCP OSCP Offensive Security
AZ-500 Azure Security Engineer Microsoft Certified
BTL2 Blue Team Level 1 + 2 Security Blue Team
CySA+ CySA+ CompTIA
Security+ Security+ CompTIA
PMRP Malware Research Professional TCM Security

Experience Forged in the Trenches

Bringing 5+ years of proven experience spanning the Department of Defense, elite military cyber commands, private sector MSSP security analysis, and advanced Azure cloud security engineering.

We Can Build the Foundation

We deploy Microsoft Sentinel, Defender for Cloud and Endpoint and Entra ID protection, run vulnerability assessments, and hand your team a working, documented setup.

Book a Consultation

Veteran-Owned · Built on the Microsoft Security Ecosystem

Microsoft Sentinel
Defender XDR
Entra ID
M365 Defender
Defender for Cloud

See Your Security Queue Worked by Agents You Control

Explore the demo with a fictional company, or connect your own Sentinel workspace for a 14-day trial.